
TL;DR: Microsoft's Agent Governance Toolkit, or AGT, turns agent policies into executable controls. It evaluates YAML policies before tool calls, message sends, and delegations reach the network; identifies the requesting agent; records the active policy, request, and decision; and raises GovernanceDenied when an action is blocked. It complements IAM and OAuth rather than replacing them.
- Treat agent governance as an enforcement boundary, not a policy document: the control must run before the action reaches the network.
- Keep identity and authorization separate. IAM and OAuth establish service access, while AGT evaluates the agent's requested action.
- Use YAML policies to express different risk treatments, including default allows, denials for drop, delete, and truncate, and approval requirements for email.
- Auditability is part of enforcement: retain the active policy, agent request, and allow-or-deny decision together.
- Do not adopt the toolkit as proof of governance if your team cannot operate identity, logging, and policy controls in production.
An autonomous agent that can call tools, send messages, or delegate work needs more than a policy document. It needs controls that run before an action reaches the network. Microsoft’s Agent Governance Toolkit: Turn AI Policies Into Enforced Controls describes AGT as infrastructure for policy enforcement, zero-trust identity, execution sandboxing, and reliability engineering for autonomous AI agents.
Microsoft’s Agent Governance Toolkit, or AGT, turns agent policies into executable controls. It evaluates YAML policies before tool calls, message sends, and delegations reach the network; identifies the requesting agent; records the active policy, request, and decision; and raises GovernanceDenied when an action is blocked. It complements IAM and OAuth rather than replacing them.
The Microsoft AI Agent Governance Toolkit repository frames governance as a control-plane problem. The useful test is not whether a policy describes acceptable behaviour. It is whether the system can enforce that policy, identify the agent making the request, and produce evidence that the decision occurred.
What does Microsoft’s Agent Governance Toolkit need to prove about an agent?
Microsoft’s Agent Governance Toolkit is built around three questions: whether an agent action is allowed, which agent performed it, and whether the event can be proven through tamper-evident records. These are separate concerns: authorization, identity, and auditability.
OAuth scopes and IAM roles control access to services, but they do not determine what an agent does after connecting. Shared API keys create another problem in multi-agent systems because they make incident attribution difficult when several agents use the same credential.
AGT records the active policy, the agent request, and the allow-or-deny decision in an audit trail. The record is therefore part of the control, not merely a report generated after the fact.
The source reports coverage of all 10 areas of the OWASP Agentic Top 10, with mappings to NIST AI RMF 1.0, the EU AI Act, and SOC 2. These are source-reported mappings with audit evidence or audit-trail export. They are not proof that an organisation is compliant or that every agent risk has been addressed.
Why are IAM, OAuth, and prompt-level safety insufficient on their own?
IAM and OAuth answer the service-access question. They do not answer whether a particular agent should perform a particular operation after access has been granted. AGT operates at that action level; it complements credentials and access controls rather than replacing them.
Prompt-level safety has a different limitation. Prompt injection and model-layer defences are probabilistic. They may influence behaviour, but they do not provide a deterministic boundary for operations that must be blocked consistently.
AGT moves enforcement into application code. That creates an operational obligation: the team must manage agent identities, maintain policies, operate logging, and handle approval or denial workflows. A governance package cannot compensate for controls that nobody can run or observe in production.
When should a team not use this toolkit as its governance answer? If it cannot operate identity, logging, and policy enforcement in production, it should not treat AGT as proof of governance. Adding a policy file to an unobservable agent system creates false confidence.
How does AGT block unauthorised agent actions?
AGT intercepts every tool call, message send, and delegation in deterministic application code before the model’s intent reaches the network. When the AGT kernel denies an action, the action is structurally blocked rather than left to a later review step.
That is the difference between an instruction and an enforcement point. A prompt can tell an agent not to send an email without approval. An application-level policy can stop the message operation and emit a denial that the surrounding system can inspect.
This boundary is specific, not universal. Deterministic interception does not solve every agent risk, and it does not make an underlying tool safe by itself. The relevant calls, messages, and delegations must pass through AGT for the control to apply.
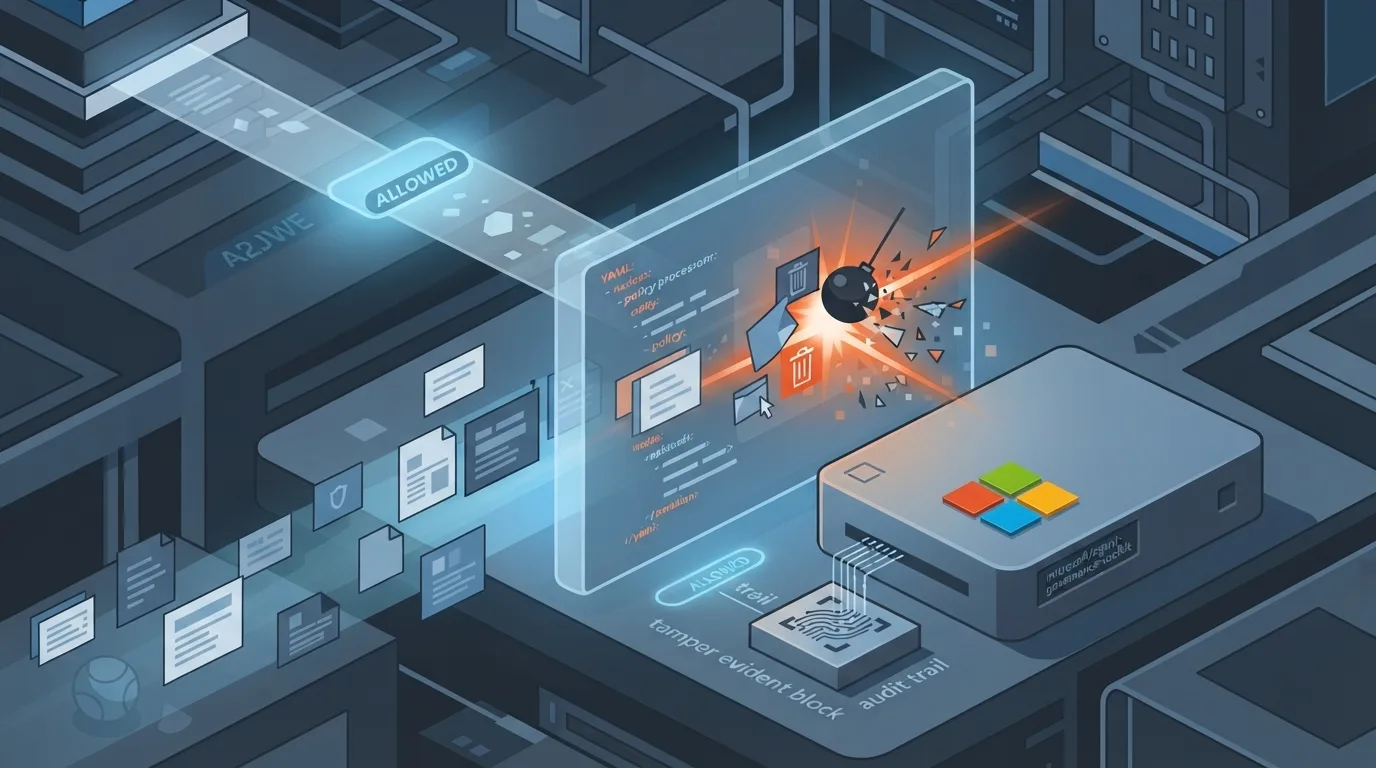
The evaluation question is straightforward: can the team map each important policy to a deterministic control that runs before the action leaves the application? If not, it has documentation rather than enforceable governance.
How do you start with the Python SDK?
The quick start requires Python 3.11 or later. Install the full package with:
pip install "agent-governance-toolkit[full]"
A tool function can be governed with two lines of Python:
from agentmesh.governance import govern
safe_tool = govern(my_tool, policy="policy.yaml")
Each call evaluates the YAML policy, writes the decision to an audit trail, and raises GovernanceDenied when the action is blocked.
The toolkit supports any framework through a single pip installation. That is useful when the engineering problem is adding a consistent governance boundary around existing tools and workflows rather than selecting a different agent framework.
Do not mistake the short integration for a complete operating model. Before expanding usage, assign ownership for agent identity, policy changes, audit records, approval paths, and enforcement failures.
What can AGT policies allow, deny, or require?
AGT policies can allow actions by default, deny destructive operations, or require approval for selected operations. The source gives three concrete behaviours:

- Allow actions by default where that policy is appropriate.
- Deny destructive operations such as
drop,delete, andtruncate. - Require approval for actions such as sending email.
Every governed call evaluates the YAML policy and records the result. When a call is denied,GovernanceDeniedgives the application a defined failure signal instead of allowing the operation to continue silently.
Approval rules introduce an operational cost because they add a human or workflow dependency to actions that might otherwise run automatically. That may be the right trade-off for sending email or another sensitive operation, but the approval path must be operated rather than merely configured.
The same applies to auditability. A blocked call is useful only if the team can inspect what was denied, which policy was active, which agent requested it, and what decision was made. AGT records those elements together, but the team still owns retention, access, and review of the audit trail.
How does the AgentControl API extend governance?
The AgentControl API provides programmatic policy evaluation beyond the Python wrapper. It includes an Agent Control Specification manifest and an agent identity envelope, giving application and platform workflows explicit artifacts for control expectations and identity context.
The toolkit also includes SDK and integration examples for TypeScript, .NET, Rust, and Go, as well as MCP server integration. Claude Code can use AGT through its plugin marketplace. These options broaden the implementation surface, but they do not remove the need to operate identities, policies, logs, and enforcement failures.
Is the toolkit suitable for every production team?
AGT is in public preview, so releases may include breaking changes before general availability. Teams evaluating it for critical agent workflows should account for version management and upgrade testing.
Evaluate the toolkit when you need executable policy decisions, agent identity, deterministic interception, and exportable audit evidence around autonomous actions. Do not use it as a substitute for an operating model your team cannot support.
Governance is credible only when controls are active, observable, and maintained. AGT can provide the enforcement mechanism and records around a decision. The team still owns the identities, policies, integrations, audit operations, and response when something is denied or misconfigured.
Frequently asked questions
Does AGT replace IAM or OAuth?
No. IAM roles and OAuth scopes control service access, while AGT evaluates what an agent does after it connects. Credentials establish access; policy enforcement determines whether a specific tool call, message send, or delegation is allowed.
Can prompt instructions provide the same protection as AGT?
No. Prompt injection and model-layer defences are probabilistic, so they are not sufficient for deterministic blocking. AGT intercepts tool calls, message sends, and delegations in application code before the model’s intent reaches the network, and denied actions are structurally blocked by its kernel.
What does AGT record for an audit?
AGT records the active policy, the agent request, and the allow-or-deny decision in an audit trail. Each governed call evaluates the YAML policy, logs the result, and raises GovernanceDenied when blocked. Teams still need to operate and retain those records appropriately.
Is the toolkit a compliance certification?
No. The source reports mappings to the OWASP Agentic Top 10, NIST AI RMF 1.0, the EU AI Act, and SOC 2. Those mappings and audit evidence can support an evaluation, but they do not certify compliance or eliminate the need for organisational controls.
Key takeaways
- Treat agent governance as an enforcement boundary, not a policy document: the control must run before the action reaches the network.
- Keep identity and authorization separate. IAM and OAuth establish service access, while AGT evaluates the agent’s requested action.
- Use YAML policies to express different risk treatments, including default allows, denials for drop, delete, and truncate, and approval requirements for email.
- Auditability is part of enforcement: retain the active policy, agent request, and allow-or-deny decision together.
- Do not adopt the toolkit as proof of governance if your team cannot operate identity, logging, and policy controls in production.
Practical tips
- Test the Python wrapper against a denied destructive operation before connecting it to a critical workflow.
- Define ownership for policy files, agent identity envelopes, approval paths, and audit-trail retention before expanding integration coverage.
- Check that every relevant tool call, message send, and delegation passes through the enforcement layer; interception only applies where traffic traverses it.
- Because the toolkit is in public preview, include breaking-change testing in the release process before upgrading.
Evaluate the control boundary
Start with one governed tool and verify the full path: policy evaluation, agent identity, denial behaviour, and audit evidence. Expand only after your team can operate those controls reliably.
Related Posts
AI Build vs Buy: Compare Five-Year Operating Cost
The AI build vs buy decision should weigh five-year operating cost, vendor…

EU AI Act Compliance Is a Portfolio-Triage Problem
Uncertain EU AI Act timing means US companies should prioritize AI uses by…
Cloud Concentration Risk: One Outage, Many AI Services
A reported Azure failure shows how shared cloud dependence can turn one outage…